
1、spring-boot-dependencies
翻译一下:Springboot多依赖。
1、前言:
在 SpringBoot 开发时,我们常常会发现一个现象:即在 pom 文件中,加入一个新的依赖,往往不需要引入相应的版本号(如下代码块所示),就可以正常引入依赖,这其实是因为我们依赖了 spring-boot-starter-parent 模块的缘故!
Java
<parent>
<groupId>org.springframework.boot</groupId>
<artifactId>spring-boot-starter-parent</artifactId>
<!-- 在这里指定了 spring boot 的版本 -->
<version>2.7.2</version>
<relativePath/> <!-- lookup parent from repository -->
</parent>
<dependencies>
<dependency>
<groupId>org.springframework.boot</groupId>
<artifactId>spring-boot-starter-web</artifactId>
</dependency>
<dependency>
<groupId>org.springframework.boot</groupId>
<artifactId>spring-boot-starter-test</artifactId>
<scope>test</scope>
</dependency>
...
</dependencies>点进去spring-boot-starter-parent发现,spring-boot-starter-parent 继承了 spring-boot-dependencies
Java
<parent>
<groupId>org.springframework.boot</groupId>
<artifactId>spring-boot-dependencies</artifactId>
<version>2.7.2</version>
</parent>再点spring-boot-dependencies进去发现
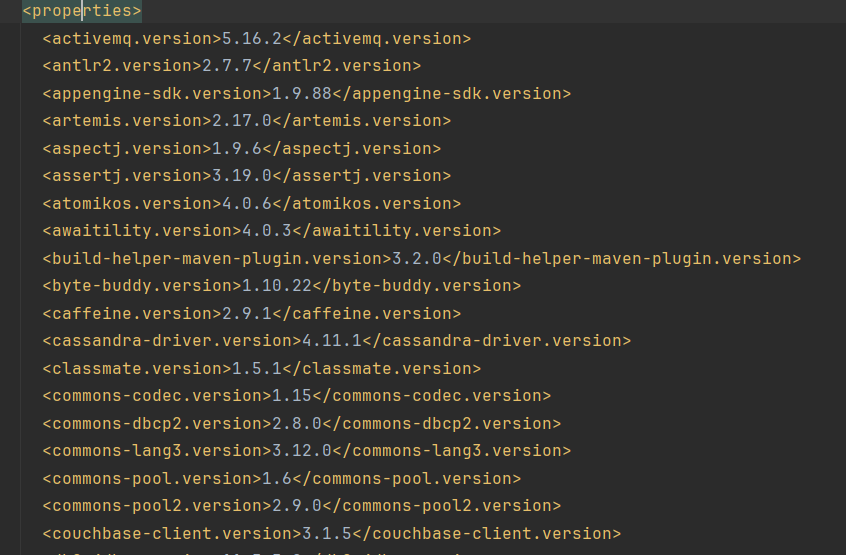
这个依赖配置很多版本号。在 dependencyManagement 进行依赖管理,在 pluginManagement 中进行插件管理:
结论就是:spring-boot-dependencies是统一管理一系列依赖的父结点。重要的是对版本各种不冲突的版本进行合并,即==版本号的控制管理==,这样不会导致引入冲突的版本导致的问题
2、借鉴思想
Xml
<!--版本号管理 start -->
<properties>
<test.version>5.5.2</test.version>
<plugin.version>5.5.2</plugin.version>
</properties>
<!--版本号管理 end -->
<!-- 依赖管理 start -->
<dependencyManagement>
<dependencies>
<groupId>xxxx</groupId>
<artifactId>xx-maven-plugin</artifactId>
<version>${test.version}</version>
</dependencies>
</dependencyManagement>
<!-- 依赖管理 end-->
<!-- 插件管理 start-->
<pluginManagement>
<plugins>
<groupId>xxxx</groupId>
<artifactId>xxxxxxx</artifactId>
<version>${plugin.version}</version>
</plugins>
</pluginManagement>
<!-- 插件管理 end-->3、总结
1、spring-boot-dependencies的作用:版本号的控制管理
2、spring-boot-starter-parent其实就是在继承spring-boot-dependencies
3、引入自主版本控制的思想:关键字<properties>:版本控制,<dependencyManagement>依赖管理、<pluginManagement>插件管理
2、spring-boot-starter-security
security服务有个问题?在启动后,取消依赖,还是会启动登录拦截器
解决方法:
自定义取消其中的登录拦截器
com/w/config/MySecurtiyConfig
Java
package com.w.config;
import org.springframework.security.config.annotation.web.builders.HttpSecurity;
import org.springframework.security.config.annotation.web.configuration.WebSecurityConfigurerAdapter;
import org.springframework.stereotype.Component;
@Component
public class MySecurtiyConfig extends WebSecurityConfigurerAdapter {
@Override
protected void configure(HttpSecurity http) throws Exception {
// 正常配置其他安全相关的内容
// 将登录框关闭
http.formLogin().disable();
}
}